Auditing your Azure architecture
A complete method to run a Well-Architected Review on Azure, turn findings into a prioritised remediation plan and manage residual risks over time.
Upgrading Kubernetes
An operational guide to absorbing the pace of three minor releases a year without a maintenance window: compatibility, cutover strategies, controlled draining and automation.
Sovereign Cloud in Europe
A practical guide to the new European regulatory framework (CADA, Cloud Sovereignty Framework, NIS2, DORA) for building a compliant, resilient, and controlled cloud strategy.
Cutting Your AWS Bill by 30 to 40%
A practical guide to combining pricing commitments, rightsizing, and automation — turning FinOps into a continuous discipline rather than a one-off audit.
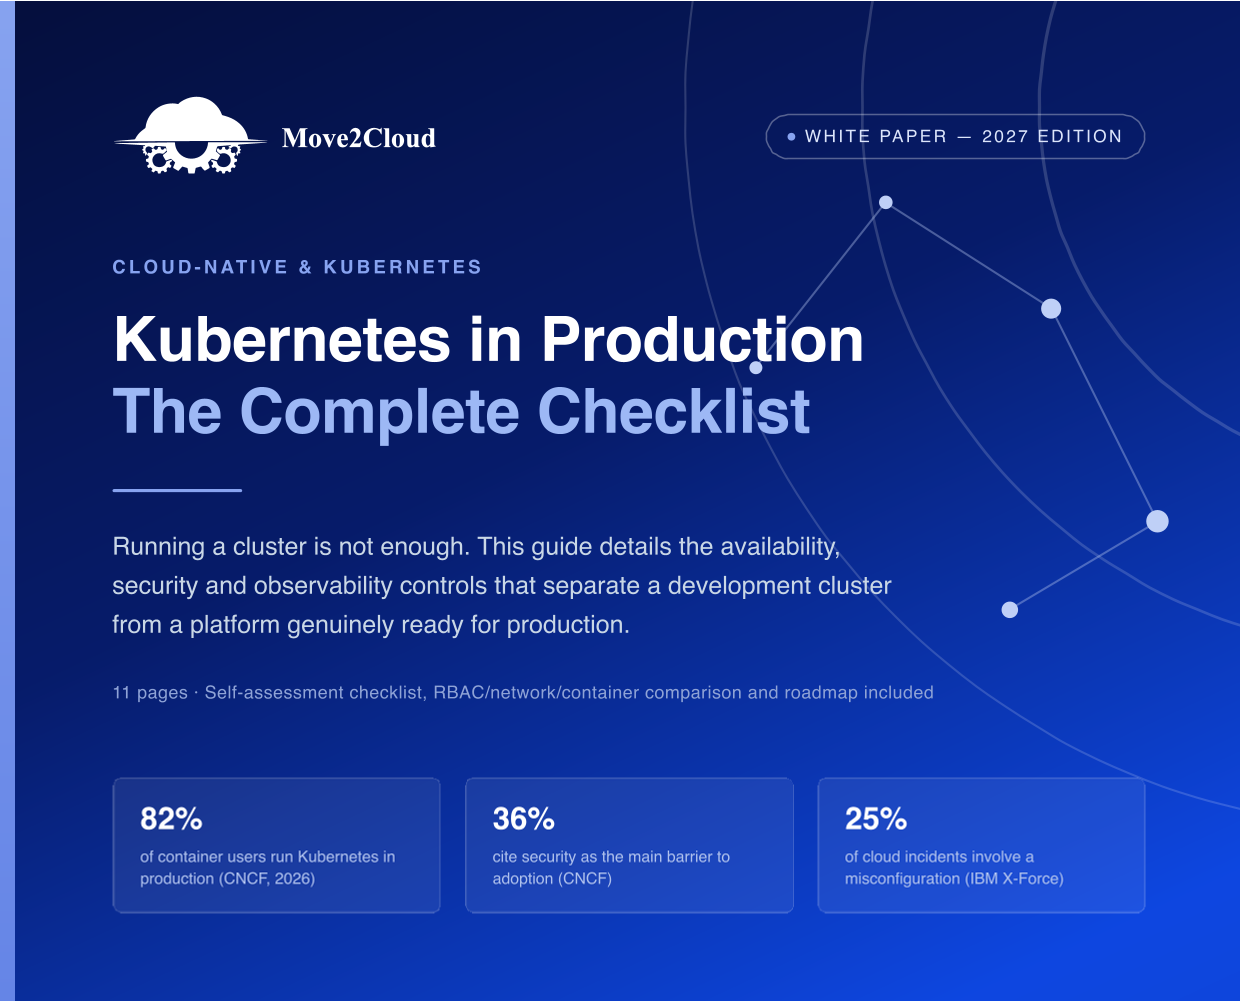
Kubernetes in Production — The Complete Checklist
Running a cluster isn't enough. This guide details the availability, security, and observability controls that separate a development cluster from a platform truly ready for production.
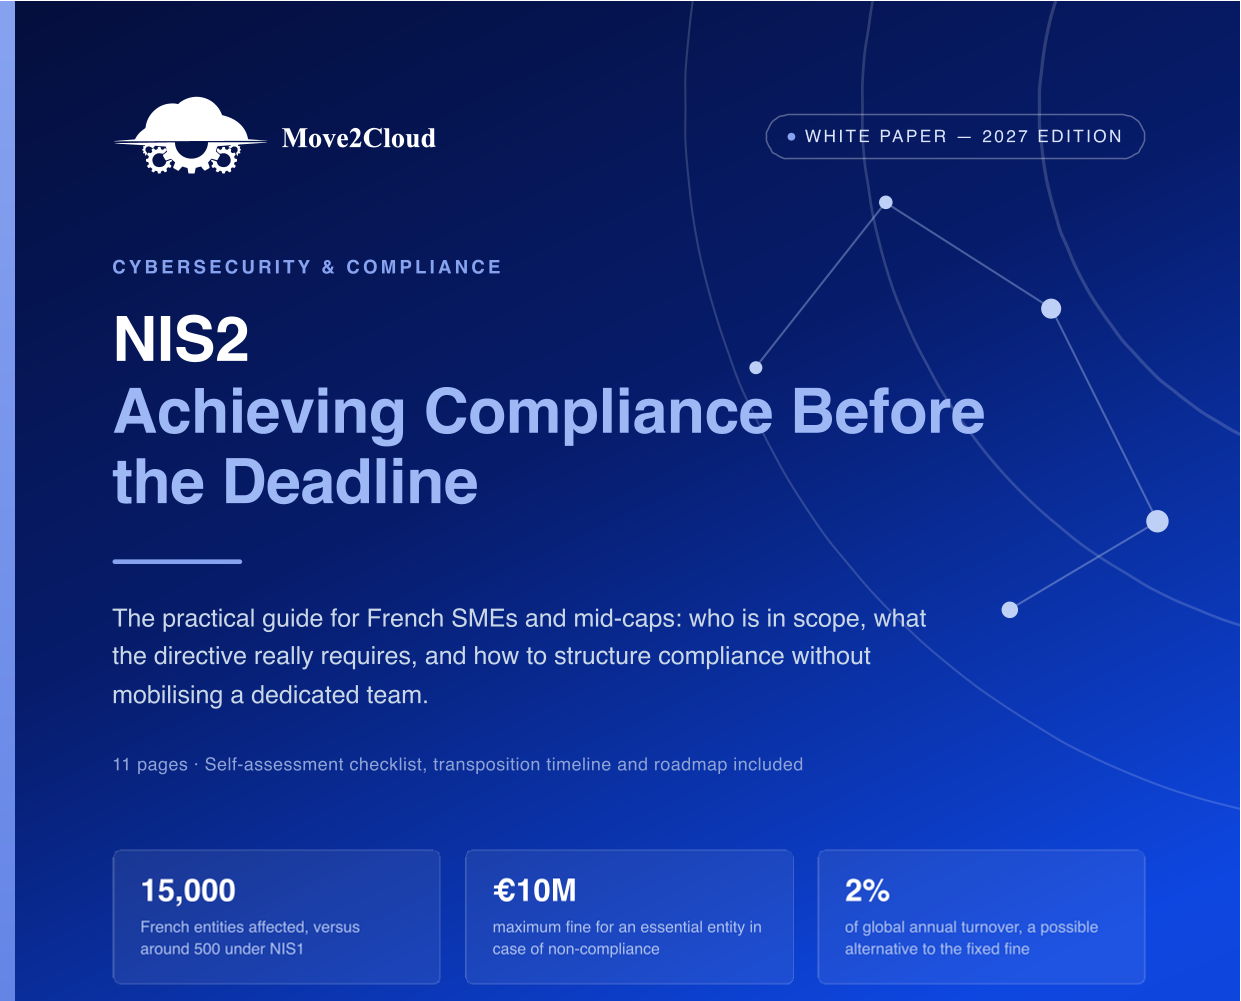
NIS2 — Becoming Compliant Before the Deadline
A practical guide for French SMEs and mid-sized companies: who is affected, what the directive really requires, and how to structure compliance without dedicating a full-time team.
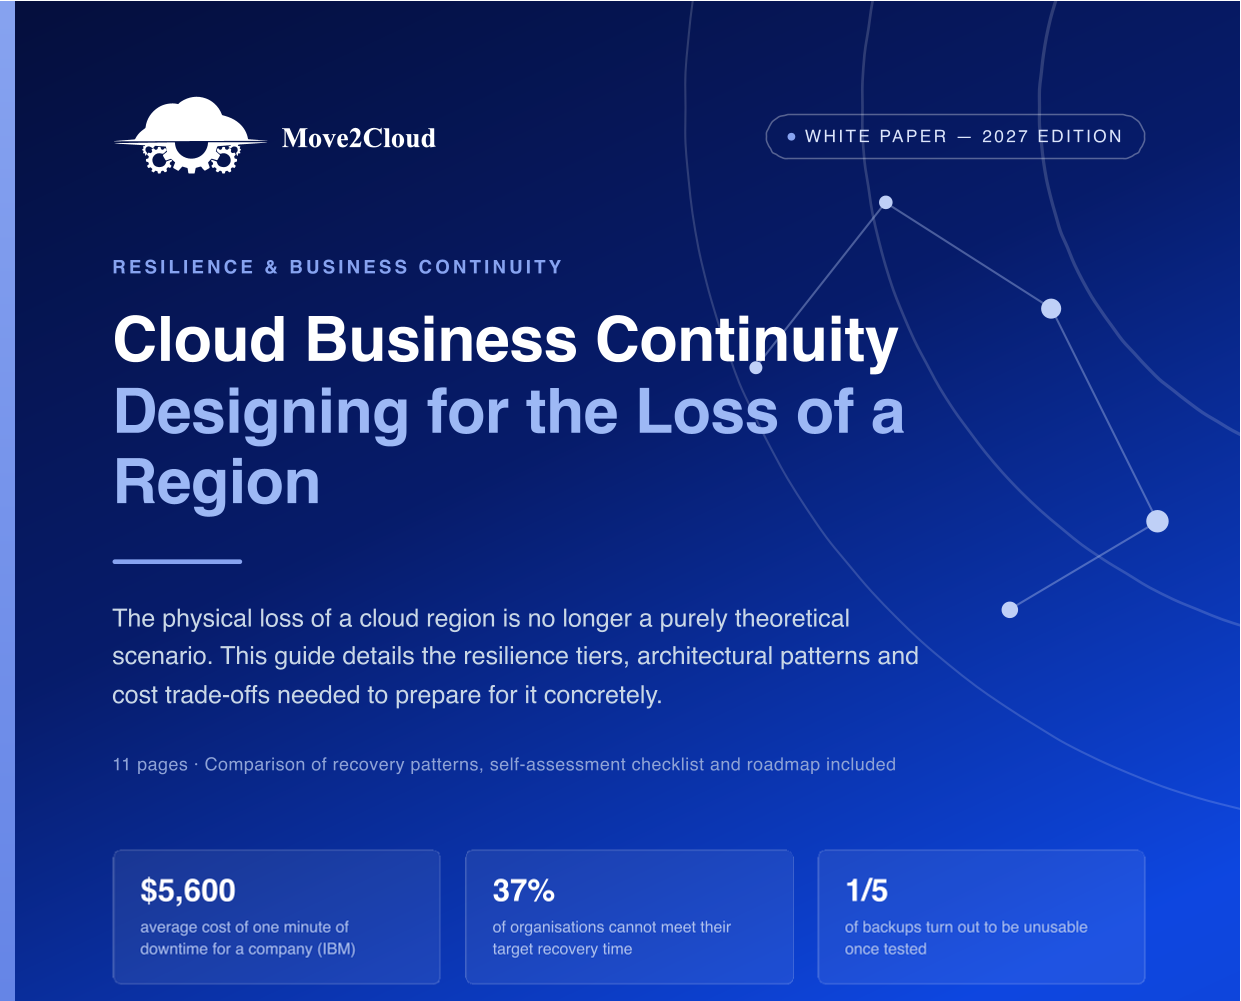
Cloud Business Continuity — Designing for the Loss of a Region
The physical loss of a cloud region is no longer a purely theoretical scenario. This guide details resilience levels, architectural patterns, and cost trade-offs to prepare for it concretely.
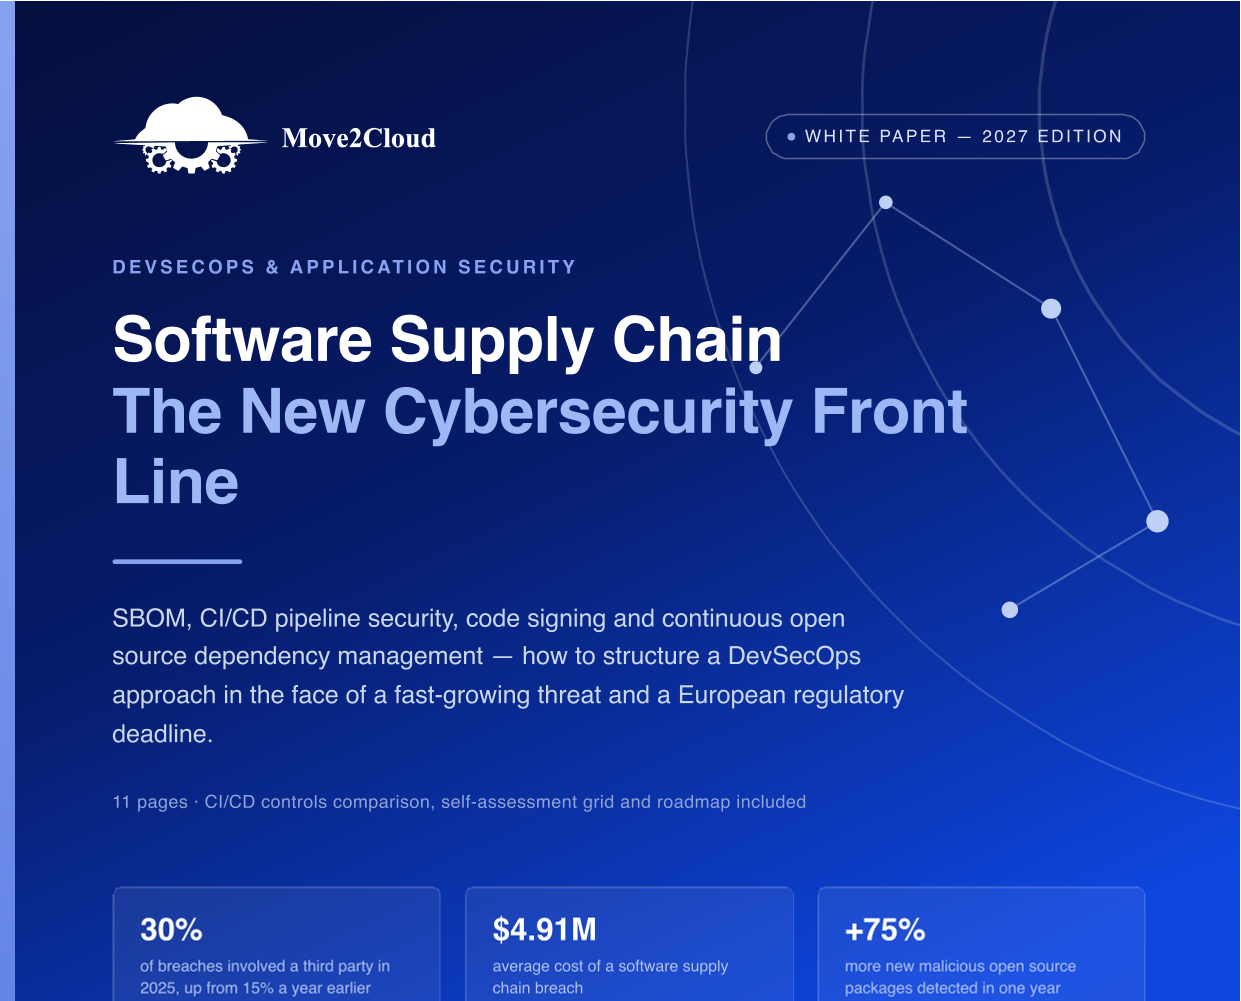
Software Supply Chain — The New Cybersecurity Frontline
SBOM, CI/CD pipeline security, code signing, and continuous open source dependency management — how to structure a DevSecOps approach in the face of a fast-growing threat and an upcoming European regulatory deadline.