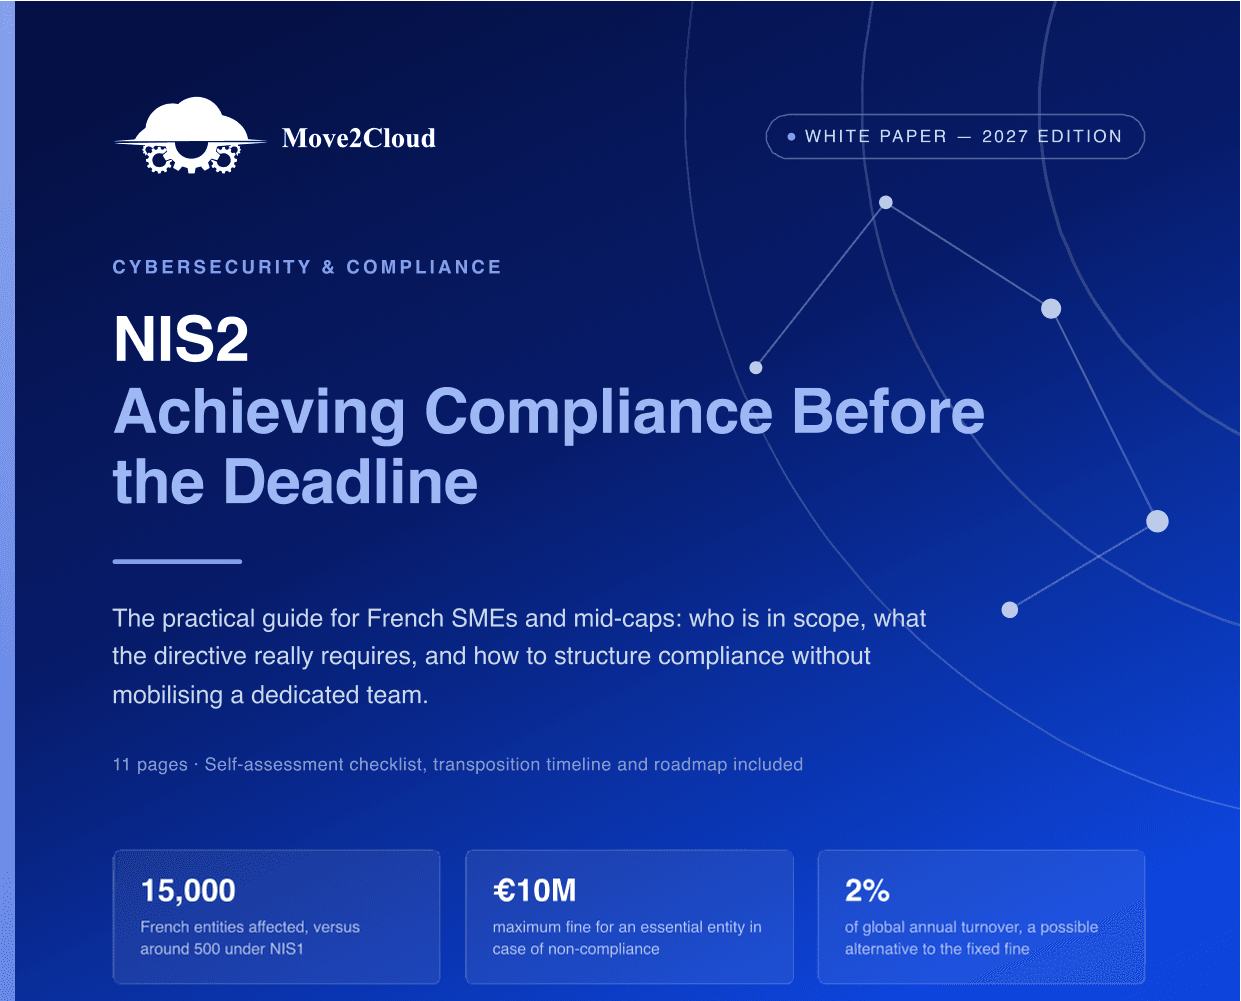
NIS2 is no longer reserved for large groups: around 15,000 French entities will be affected, compared to around 500 under the former NIS1 regime — a thirtyfold increase in scope.
Penalties are sized to be dissuasive: up to €10 million or 2% of worldwide turnover for an essential entity in default, with liability that can reach up to the executives themselves.
Am I affected? Sectors, thresholds, categories
Three combined criteria determine whether an entity is subject to the directive: its sector of activity (18 sectors split into two criticality levels), its size, and the resulting criticality level.
An SME with fewer than 50 employees can still be affected if it is the sole identified critical supplier of an essential entity.
What NIS2 actually requires
Documented risk analysis, an incident notification procedure within 24h then 72h, a tested continuity plan, and an assessment of supplier security.
Direct involvement of governing bodies in cyber risk management, with formal approval of the measures.
Key takeaways
- Check whether the sector appears in one of the directive's two annexes
- Check whether headcount or turnover exceeds the applicable thresholds
- Have a formalized incident detection and notification procedure within 24h
- Have tested the business continuity plan within the last twelve months
- Have trained executives on their cyber risk management responsibilities